Codex YOLO Mode: Run Without Approvals Safely
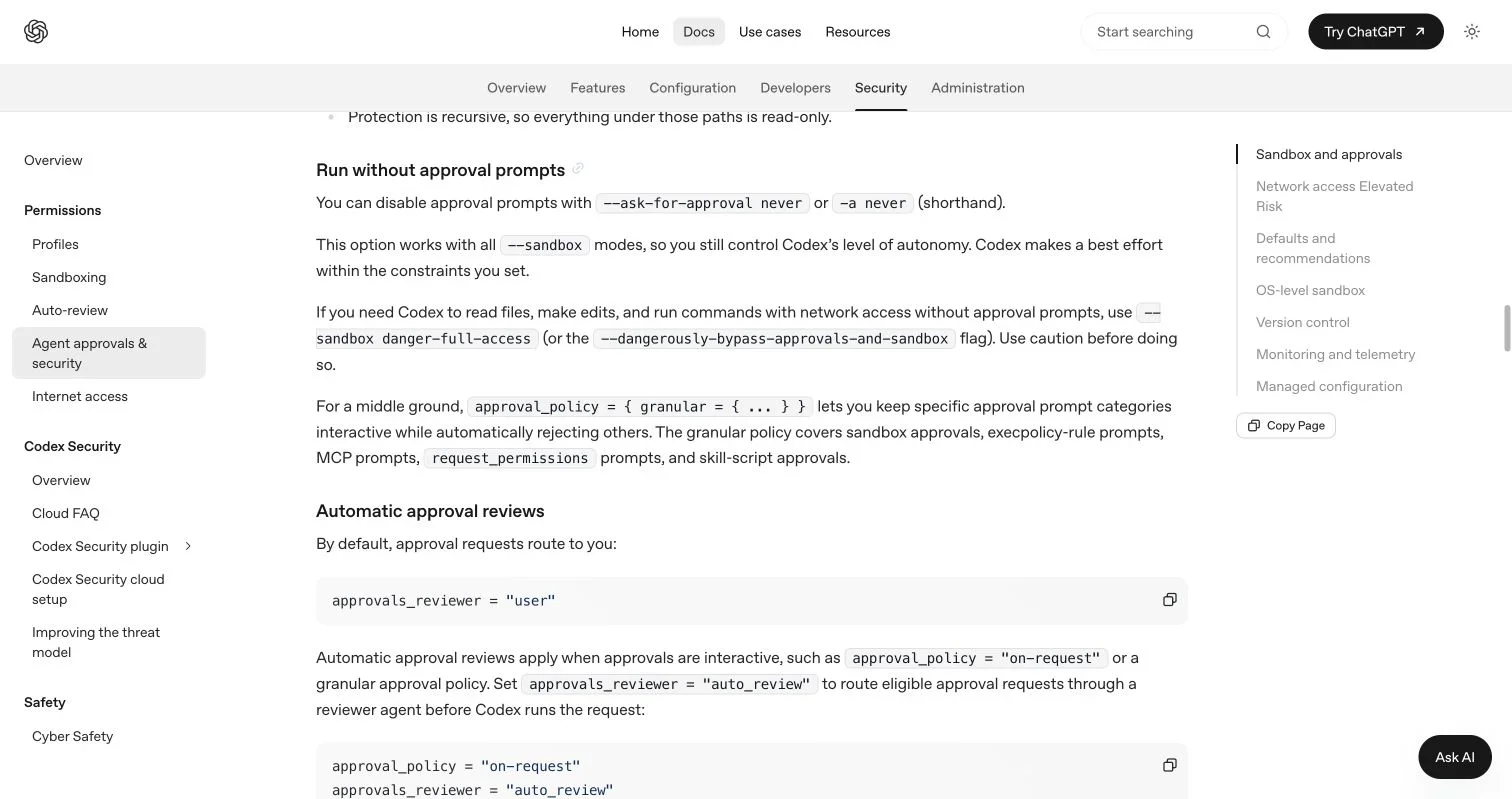
Codex YOLO (You Only Live Once) mode is the risky way to run the Codex CLI when you want the agent to keep working without approval prompts. It’s shorthand for a setup where the agent has broad local access and doesn’t stop to ask before running commands.
The command is:
codex --sandbox danger-full-access --ask-for-approval neverThat combination matters because Codex has two separate controls. The sandbox mode controls what commands can access. The approval policy controls when Codex must pause and ask before acting. --sandbox danger-full-access removes the usual sandbox boundary. --ask-for-approval never tells Codex not to stop for approval prompts.
OpenAI also documents the --yolo flag, also known as --dangerously-bypass-approvals-and-sandbox, for running every command without approvals or sandboxing. The official CLI reference says to use it only inside an externally hardened environment. If you’re not already inside a disposable or tightly controlled environment, this mode is probably too permissive.
How to tell that YOLO mode is on
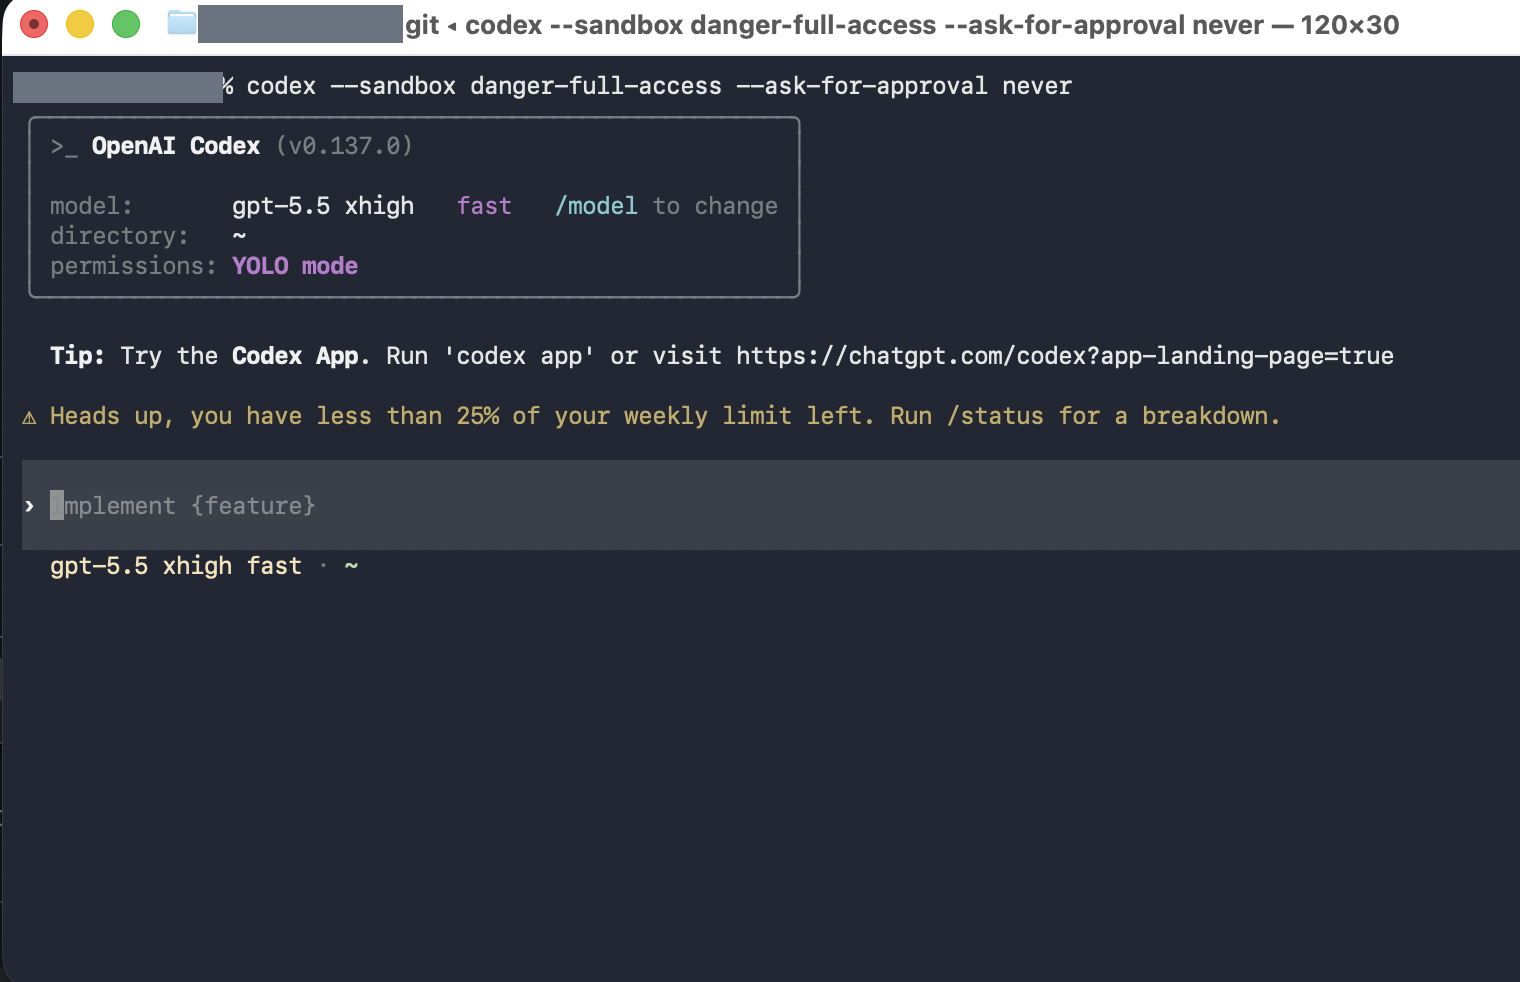
The screenshot below shows the Codex terminal after launch. The key line is permissions: YOLO mode, the indicator that the dangerous/no-approval mode is active.
The command at the top shows the exact launch form: codex --sandbox danger-full-access --ask-for-approval never. If you see permissions: YOLO mode, assume Codex can act quickly and broadly until you stop it.
Who should use it
Use it only if you are an experienced user who understands the project, the shell, the current working directory, and the credentials available to the process. This is not a good default for learning Codex, looking at an unfamiliar repository, reviewing untrusted code, or working near production infrastructure.
You should know what package-manager scripts do in the repo, which cloud CLIs are installed and authenticated, and whether .env files, SSH keys, API tokens, database credentials, or deployment config are reachable from the session. You should also be comfortable reading git diff after the agent works.
What Codex can do without approvals
In this mode, Codex can do much more damage than in a normal workspace-write session with approvals. The exact blast radius depends on your machine and config, but the risk categories are clear:
- Modify, overwrite, or delete files in places available to the process.
- Run shell commands without pausing for confirmation.
- Run package-manager commands such as
npm,pnpm,pip,bundle, orcargo, or execute project-specific scripts. - Rewrite git history if asked, or if a command it runs does so.
- Touch additional directories exposed by the current user or by Codex configuration.
- Use network access if this mode or the environment allows it.
- Read secrets available through environment variables, local config, credential files, or mounted directories.
- Run destructive database, deployment, cloud, or infrastructure commands if those tools are installed and authenticated.
- Follow malicious instructions embedded in untrusted project files, docs, webpages, or tool output.
- Make many changes before a human notices the direction is wrong.
That last point is underrated. Approval prompts aren’t only a security feature; they also control the pace. They force you to notice when the agent crosses a boundary. Skipping approvals removes that pacing.
Safer alternatives
For most local development, use the safer sandbox mode with on-request approvals:
codex --sandbox workspace-write --ask-for-approval on-requestThat lets Codex edit and run routine commands inside the workspace, while still asking when it needs to cross the boundary. If you want planning without changes, run Codex with --sandbox read-only. If you want automation, isolate it.
A safer pattern looks like this:
- Create a throwaway branch.
- Run in a disposable VM, dev container, or sandboxed machine.
- Remove production credentials from the environment.
- Avoid exposing your home directory or unrelated repositories.
- Keep cloud CLIs logged out unless the task needs them.
- Let Codex work on a narrow task, then inspect
git diffbefore continuing. - Run tests yourself before merging or deploying.
YOLO mode can be useful in a hardened environment where the agent runs many commands without friction. It is a poor fit for a normal laptop session with broad credentials and a messy working tree.
Where the safety has to come from
The right mental model is not “Codex is trusted now.” The right model is “I moved the trust boundary outside Codex.” If you run Codex with danger-full-access and ask-for-approval never, your safety has to come from the surrounding environment: container limits, VM snapshots, branch isolation, credential isolation, network policy, and human review after the run.
If the environment is not hardened, do not compensate with hope. Use a safer sandbox mode and keep approval prompts on.
Related
Claude Code has a similar YOLO-style workflow through claude --dangerously-skip-permissions. See the companion article: Claude Code YOLO Mode: Using –dangerously-skip-permissions.
For official reference, see OpenAI’s Codex agent approvals and security documentation.
A docs portal with Ask AI
and support tickets
Connect a repository, or describe your product to start. Each docs site has search, Ask AI, an API console, an MCP server and support tickets.
- Publishes from GitHub on every push
- Works with Mintlify repositories
- API console from your OpenAPI file
- MCP server and llms.txt for AI agents
- Ask AI and support tickets
- Analytics for people and AI agents
History
- June 9, 2026 — Published by Revdoku Content Team
- June 7, 2026 — Reviewed by Eugene Mi
- October 20, 2026 — Last updated by Revdoku Content Team.