Claude Code YOLO Mode: What The Flag Means
Claude Code has no official YOLO (You Only Live Once) mode. Developers use the name for running Claude Code without permission prompts, so the agent keeps working without asking first. The command is:
claude --dangerously-skip-permissionsAnthropic’s Claude Code CLI reference describes --dangerously-skip-permissions as a flag that skips permission prompts and should be used with caution. Permission prompts are a control point between the agent’s plan and real changes to your files or system. Skipping them speeds up the session but removes a useful interruption point.
Use this only if you understand the repository, shell, tools Claude Code can call, and credentials in the environment.
How to tell that a session skips prompts
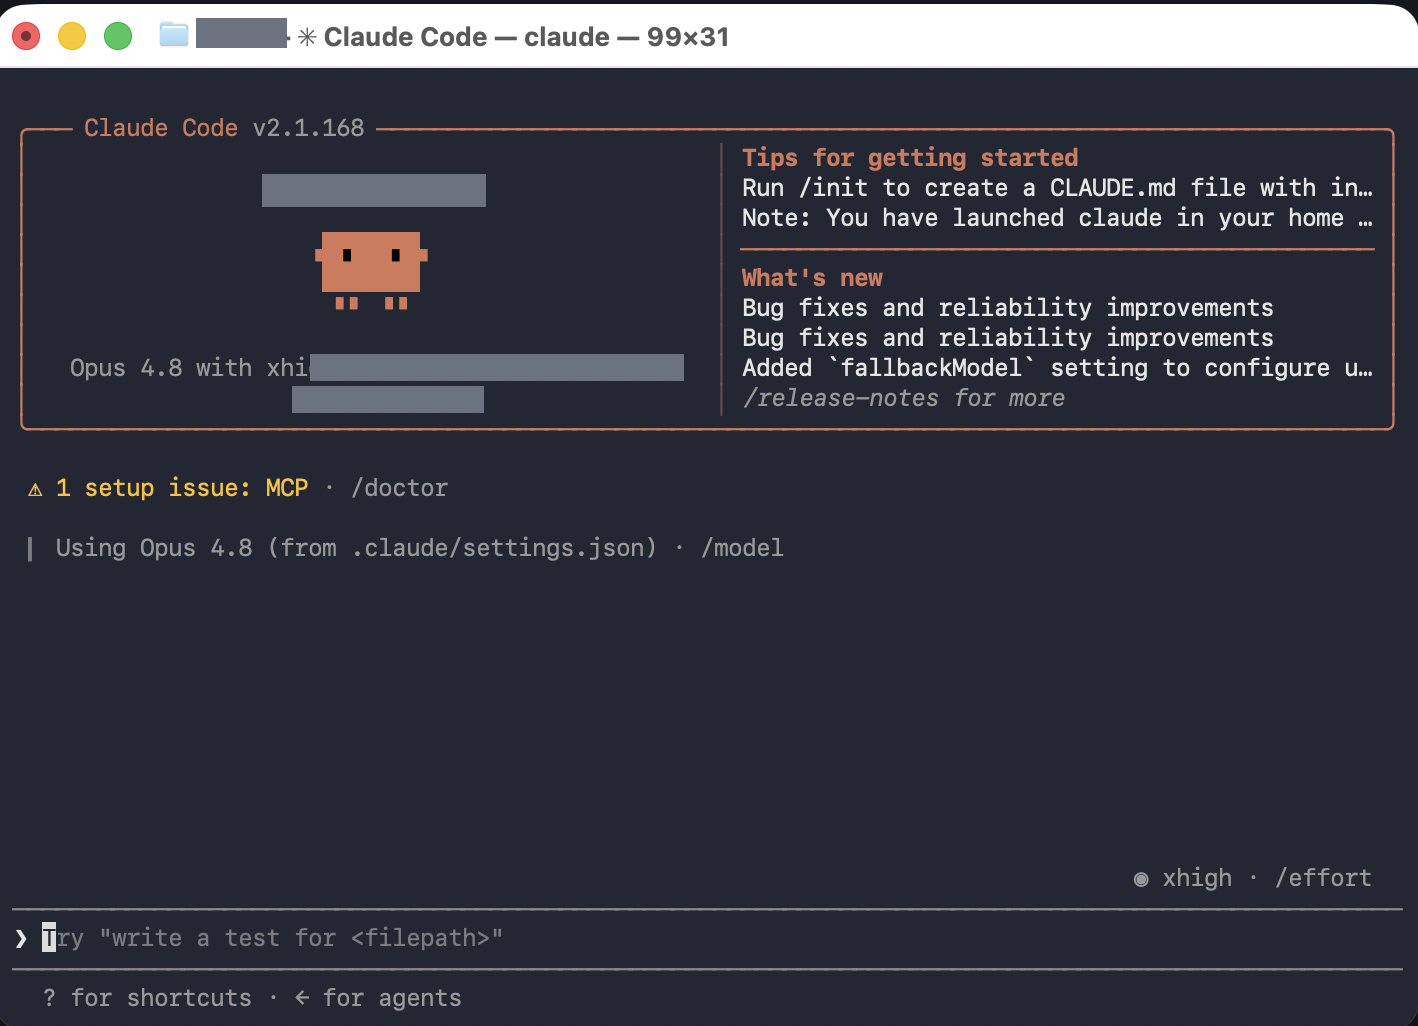
The screenshot below shows a Claude Code session started with --dangerously-skip-permissions. The CLI state is the visible review cue, but the launch command is the source of truth: if the session started with claude --dangerously-skip-permissions, treat it as a YOLO-style session.
Compared with Codex, Claude Code may not show a large YOLO mode label, so operator discipline matters more. Confirm how the session was launched before trusting it near sensitive files or production credentials.
Who should use it
It is for experienced users who know what the session exposes: the repo layout, package scripts, MCP or tool permissions, local config files, and any cloud or deployment tools in the terminal.
Don’t make it your default Claude Code startup command or everyday permission setting. Don’t use it on an unfamiliar codebase or in a directory containing production secrets, customer data, private SSH keys, or deployment credentials unless the environment is deliberately isolated.
The main question: if Claude Code ran a command without asking, would you understand the impact? If not, keep normal Claude Code CLI permissions on.
What Claude Code can do without prompts
The blast radius depends on your machine, repository, tools, and authentication state. In a permissive working directory, skipping prompts allows fast, broad changes:
- Modify, overwrite, or delete project files.
- Execute shell commands through available tools.
- Run package scripts, test scripts, migration scripts, or project automation.
- Create large diffs before you inspect them.
- Change local configuration files or generated assets.
- Use credentials from environment variables, dotfiles, local CLIs, or mounted directories.
- Run deployment, database, cloud, or infrastructure commands if those tools are installed and authenticated.
- Follow malicious instructions from project files, dependency output, issue text, docs, or webpages.
- Call MCP tools with more authority than you intended if configured broadly.
- Make seemingly irreversible changes that can be undone only with version control or backups.
Permission prompts slow the workflow but force you to notice boundary crossings. Skip them, and you take responsibility for enforcing every boundary outside the agent.
Safer alternatives
Start with normal Claude Code permissions for regular work. Use plan mode when you want the agent to reason before editing. Scope the working directory tightly. Avoid launching from your home directory or a folder containing unrelated repositories and secrets.
A safer setup:
- Use a throwaway branch.
- Run inside a dev container, disposable VM, or isolated workspace.
- Keep production credentials out of the session.
- Disable or narrow MCP tools that are not needed for the task.
- Review package scripts before allowing an agent to run them freely.
- Inspect
git diffafter every meaningful chunk of work. - Run tests and deployment steps yourself unless the environment is disposable.
If you need automation without prompts, move the risk boundary outward. The safe version of YOLO is not “trust the agent more.” It is “make the environment disposable enough that fast agent action is acceptable.”
When skipping prompts makes sense
There are legitimate uses. A hardened container with no secrets, no production network access, and a clean branch is a good place to let Claude Code work without constant prompts. Batch refactors, generated test updates, local formatting, and repetitive migration work benefit from fewer interruptions.
The mistake is skipping prompts on a normal developer laptop where the shell has access to real tokens, cloud accounts, and years of local files.
Related
OpenAI Codex has an explicit YOLO-style setup using codex --sandbox danger-full-access --ask-for-approval never, and its terminal can show permissions: YOLO mode. See the companion article: Codex YOLO Mode: Run Without Approvals Safely.
For official reference, see Anthropic’s Claude Code CLI documentation for --dangerously-skip-permissions and permission modes.
A docs portal with Ask AI
and support tickets
Connect a repository, or describe your product to start. Each docs site has search, Ask AI, an API console, an MCP server and support tickets.
- Publishes from GitHub on every push
- Works with Mintlify repositories
- API console from your OpenAPI file
- MCP server and llms.txt for AI agents
- Ask AI and support tickets
- Analytics for people and AI agents
Frequently Asked Questions
Does plan mode replace permission prompts?
Not exactly; they solve different problems. Plan mode lets the agent reason about an approach before editing, while permission prompts gate the actual file and shell actions. For most work, keep normal permissions on and use plan mode when you want to review the strategy first.
History
- June 11, 2026 — Published by Revdoku Content Team
- June 7, 2026 — Reviewed by Eugene Mi
- October 20, 2026 — Last updated by Revdoku Content Team.